Security and Quality Certifications and Standards
At Atamis, we are committed to excellence in all aspects of our business, from data security to sustainability.
As a leading provider of procurement software, we understand the importance of maintaining the highest standards in both areas. That’s why we are proud to showcase our accreditations, which reflect our dedication to protecting sensitive information. Explore our certifications below to learn more about how we uphold industry-leading practices in data security.
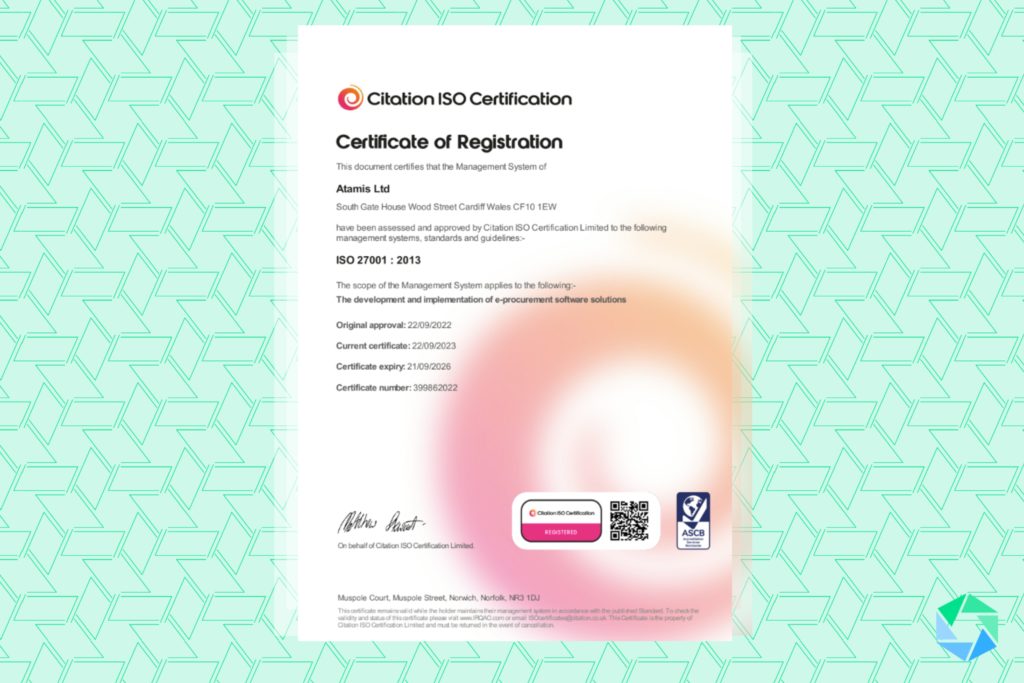
ISO27001:2022 – Information Security Management System (ISMS)
We are certified under ISO 27001, a globally recognised standard for managing risks to the security of information. This ensures that we have established comprehensive security controls to protect sensitive data.
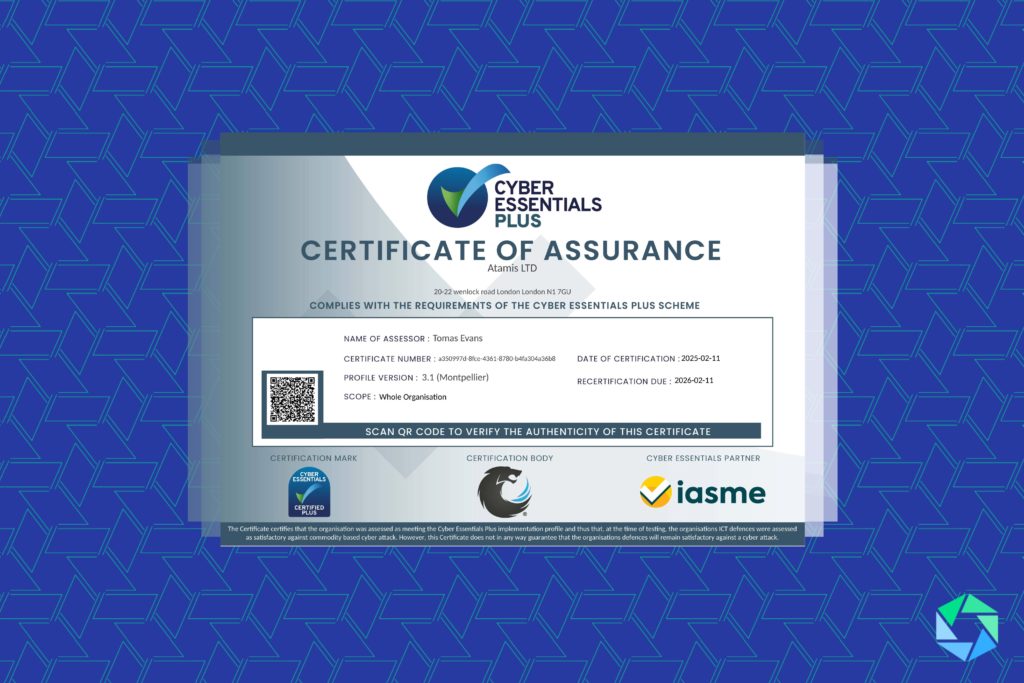
Cyber Essentials Plus
We are proud to be certified under Cyber Essentials Plus, a government-backed scheme that ensures our organisation has implemented robust cybersecurity measures to protect against a wide range of online threats.
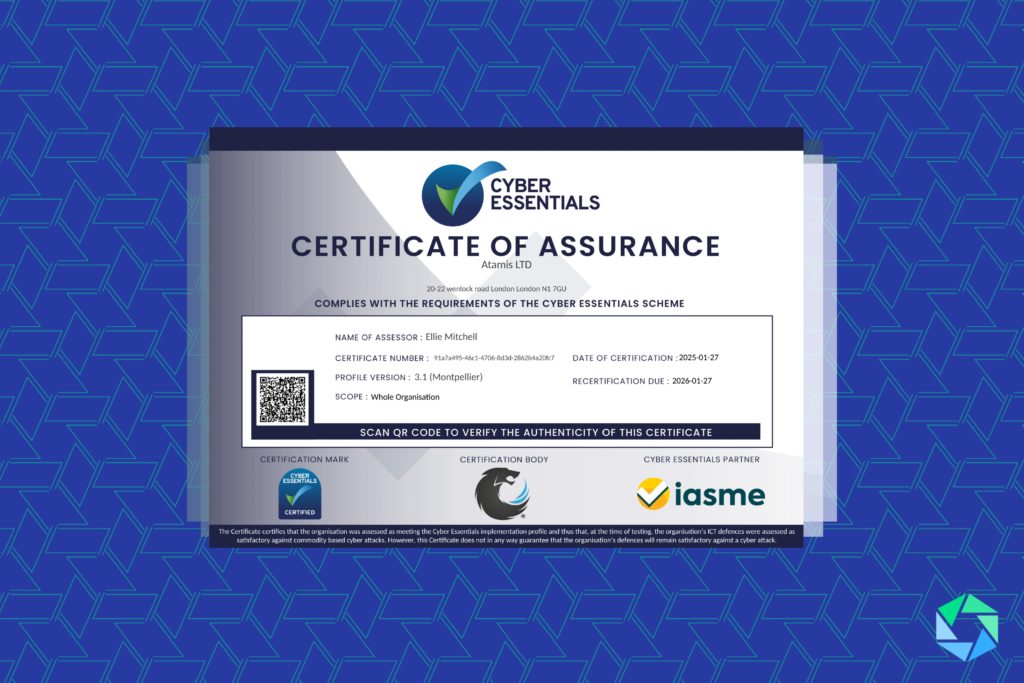
Cyber Essentials
At Atamis, we are committed to maintaining the highest standards of cybersecurity to protect our systems, data and customers. As part of this commitment, we adhere to the Cyber Essentials framework, ensuring robust security measures are in place to safeguard against cyber threats. By following these best practices, we demonstrate our dedication to security, compliance and trust.
Data Encryption Standards
Atamis is hosted on the Salesforce platform, all sensitive data is encrypted in transit using AES-SHA 384 and TLS 1.3 protocols to ensure maximum protection against unauthorised access.

GDPR Compliance (General Data Protection Regulation)
We adhere to GDPR standards to ensure the protection of personal data for our clients and users within the European Union.
Learn more
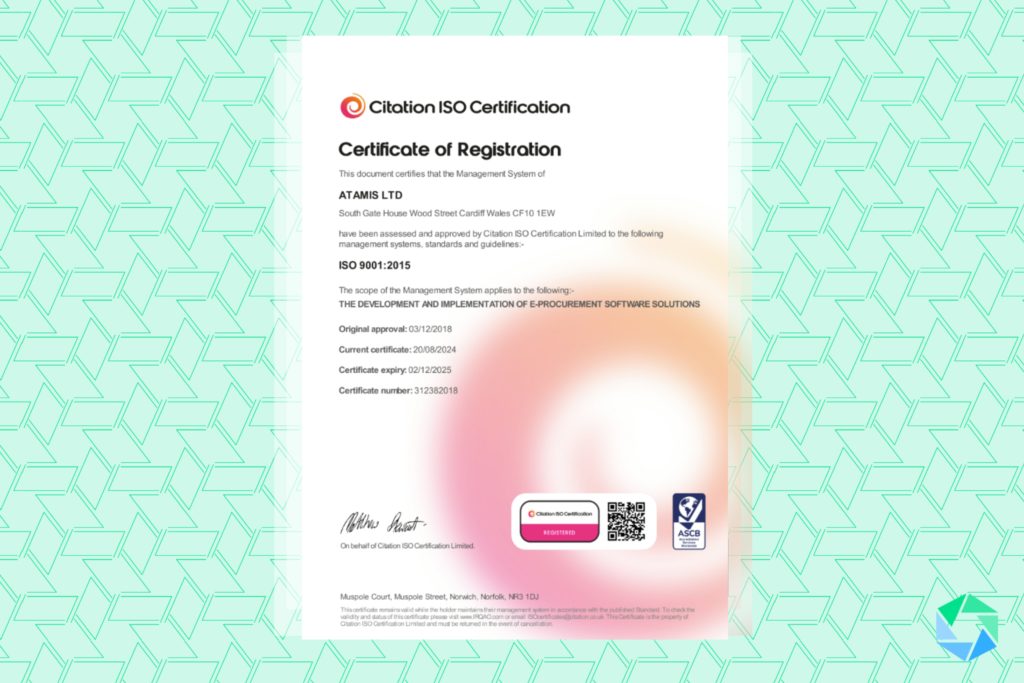
ISO 9001:2015 – Quality Management System
At Atamis, we focus on continuous improvement and delivering high-quality products and services that meet customer expectations.
Our Commitment to Security, Trust & Quality
At Atamis, security, quality and good governance aren’t simply about achieving certifications — they’re about the trust our clients place in us.
I believe we have a responsibility to be good custodians of our clients’ data, to understand and manage risk, to be transparent and accountable, and to continually improve the way we operate.Security and quality should be built into the decisions we make, the technology we use and the services we deliver — never treated as an afterthought.
Our ISO 27001, ISO 9001, Cyber Essentials and Cyber Essentials Plus certifications provide independent assurance of that commitment, but our responsibility goes beyond compliance. It’s about doing the right thing, protecting our clients and earning the trust they place in Atamis every day.
Mark CorbisieroHead of IT & Business Support